
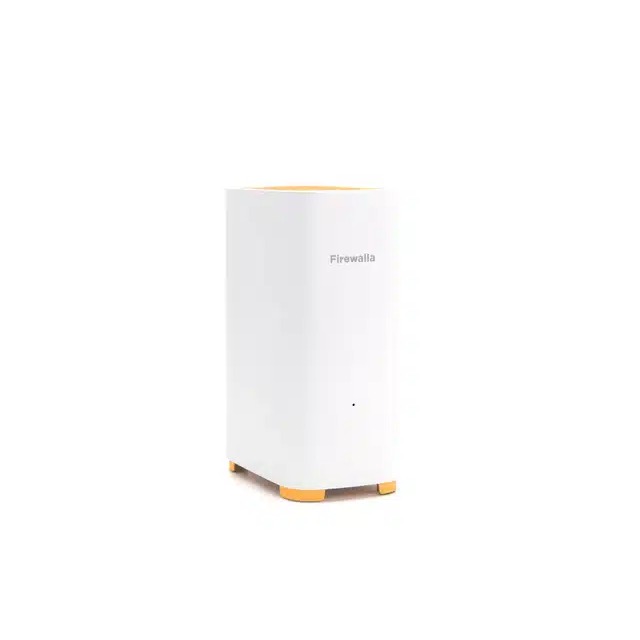


Compatibility Requirements:
-
- Gold, Gold Pro, Gold Plus, Gold SE
- Purple, Purple SE
- Firewalla must operate in Router mode.
- Can mesh with AP7 Ceiling Unit
- Availability: USA customers only.
- Shipping: 1 to 2 days after payment
- Installation: After you receive the unit, please follow this installation guide
An access point that belongs to your firewall
This is not a general-purpose wireless router. It is a Wi-Fi 7 access point designed to be managed by a Firewalla firewall, which means the policy you write once — segments, per-device rules, blocked destinations, schedules — follows a device onto the wireless network instead of stopping at the cable.
That is the whole argument for buying access points from the same ecosystem as the firewall. A third-party mesh system will give you coverage, but the firewall then sees a cloud of devices behind another router and loses much of the per-device visibility that made it worth having. Matched access points keep one policy surface and one device list.
What Wi-Fi 7 actually changes
The headline speeds are the least interesting part for most buyers. What matters in a dense home or a working office is how the standard handles congestion: wider channels and improved scheduling mean many devices sharing the air interfere with each other less, which shows up as fewer stalls and more consistent latency rather than a bigger number in a speed test.
Be realistic about the gains. A Wi-Fi 7 access point serving mostly older client devices delivers the improvements those clients can use and no more, and your internet connection remains the ceiling for anything leaving the building. The upgrade pays off most clearly where device density is high or where an existing network stalls under load.
Placement is most of the outcome
Coverage is decided by where the access points go, not by how powerful they are. A few principles that hold in almost every building:
- High and central beats hidden. Signal spreads outward and downward; an access point on a shelf at floor level behind furniture is working against itself.
- More access points at lower power beats one at maximum. A client device has a small antenna and limited transmit power; if it can hear the access point but the access point cannot hear it well, you get a strong signal indicator and a poor connection.
- Plan for the building’s materials. Tile, stucco with wire lath, brick, concrete and mirrors all attenuate heavily — common construction in Arizona and a frequent reason coverage maps drawn from square footage alone disappoint.
- Wire them where you can. A wired backhaul to each access point always outperforms a mesh link, because a mesh hop spends airtime that clients could have used.
Zero trust, in practical terms
The useful version of “zero trust” on a small network is simple: no device is trusted merely because it is connected. Each one belongs to a segment, and each segment has explicit rules about what it may reach. When the access points understand those segments, a camera joining by Wi-Fi lands in the unmanaged-device network automatically rather than sitting beside your file server.
Set the structure up as you deploy: staff or household devices; unmanaged devices such as cameras, speakers, thermostats and printers; vendors or contractors; and guests, isolated and capped. The default between segments should be deny, with exceptions written deliberately. This configuration — not the hardware — is what limits how far an incident travels.
Guest wireless done properly
A guest network that shares the main network with a different password is not a guest network. Give visitors internet access only, no visibility of internal devices, and a bandwidth limit. Put vendors there too, rather than on the staff network, and rotate the credential periodically. This takes ten minutes and closes a door that gets used more often than most owners expect.
What an access point cannot do
It extends the reach of your policy; it does not add new protection of its own. Encrypted traffic is still opaque, devices that leave the building are still outside your perimeter and need endpoint protection, cloud accounts are still defended by multifactor authentication rather than by your network, and backups remain the control that determines a ransomware outcome.
Deployment checklist
- Run cable to each access-point location if at all possible before mounting anything.
- Confirm your switch or firewall supplies the power standard this model expects — check the specification above.
- Define segments and rules before joining devices, so they land in the right place the first time.
- Walk the space with a phone after install and fix weak areas with placement before adding hardware.
- Keep firmware current on the access points as well as the firewall.
If you are planning a wider build-out, the free Cyber Risk Check will tell you which layer to spend on first, and the buyer’s guide covers how the firewall models differ.
Want it installed, monitored and patched for you? Managed Network & Infrastructure →
Reviews
There are no reviews yet.