
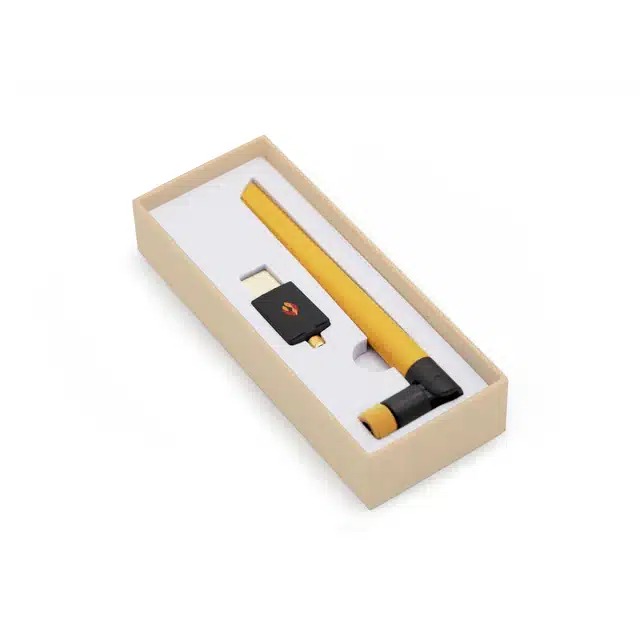


The Firewalla WiFi SD can be used in conjunction with the Firewalla Gold (both Original & Rev B Models), Gold SE, Gold Plus, Gold Pro, Purple SE, and future Gold products to enable you to tether to your phone (or another WiFi hotspot) when your main network is down and have the Firewalla Multi-WAN support automatically swap your primary internet (and automatically swap back once your primary internet is up).
One box instead of two
The Wi-Fi SD answers a specific question: can I get real network security without adding another device to a space that has nowhere to put one? It combines the firewall and the wireless access point, which suits apartments, condos, small suites, rental properties, short-term-let units and any site where a utility closet is a hopeful term for a shelf.
The trade-off is the usual one for combined units. A single device covers a single area well, and coverage in a larger or oddly shaped space is better served by a separate firewall with access points placed where people actually are. If your floor plan is open and under roughly fifteen hundred square feet, the combined unit is the simpler and better answer.
What you gain over an ISP router
The first gain is visibility. A named inventory of every connected device, what it talks to, and how much it transfers, is something no provider-supplied router offers, and it is where every other improvement begins. The second is control: rules that a consumer router cannot express, applied per device — this camera reaches the internet but nothing internal; this tablet has no internet after bedtime; this smart speaker talks to its manufacturer and nowhere else.
The third is intrusion prevention and DNS-level filtering, which block connections to known-malicious infrastructure and strip ads and trackers across every device on the network, including the ones that can never run an ad blocker — televisions, consoles, appliances, thermostats.
Wireless placement still decides the experience
A combined unit’s Wi-Fi is only as good as where you put it. Central and high beats tucked behind a cabinet every time; the router is not a decorative object and hiding it in a media console under a television costs real coverage. Keep it away from large metal appliances, mirrors and the back of a refrigerator, all of which are effective at absorbing or reflecting signal.
In a two-storey home, mounting or placing the unit high on the lower floor typically serves both floors better than putting it at ground level. If one room remains stubbornly weak after placement is optimised, that is a coverage problem an extra access point solves and a more powerful single box does not.
Rental properties and short-term lets
This unit is well suited to a property you rent out, and there is a right way to configure it. Give guests an isolated network with internet access only, no visibility of any other device, and a bandwidth cap so one visitor does not consume the connection. Keep property systems — cameras covering exterior common areas, thermostats, locks — on a separate segment guests cannot see or reach.
Two things not to do. Do not place cameras in or facing any private interior space; that is unlawful in Arizona and nearly everywhere else regardless of disclosure, and it is the fastest route to a criminal matter. And do not monitor guest traffic content — you have neither the right nor a reason, and the visibility this unit gives you is for securing the network, not for watching people who are paying to stay in it.
A small office or a home that has become one
If work happens here, a few configuration decisions matter more than the hardware. Put work machines on their own segment away from household or guest devices. Use the built-in VPN server for remote access instead of forwarding any port to an internal machine — forwarded remote-desktop ports remain one of the most reliably exploited small-business configurations there is. And make sure the work laptop still has endpoint protection, because the moment it leaves the building the firewall is behind it.
What it does not cover
It does not read inside encrypted traffic, which is nearly all of it. It does not defend a device that is not on this network. It does not protect an email or cloud account, which is defended by multifactor authentication rather than by anything at your perimeter. And it does not back anything up, which is the control that decides whether a ransomware event is a bad day or a catastrophe.
Setup and upkeep
- Put the provider’s modem or gateway into bridge mode where the carrier allows it, so you are not running two layers of address translation.
- Rebuild any port forwards as VPN access instead.
- Create the guest network on day one, isolated and capped.
- Tune alerts in the first week down to what you will act on.
- Apply firmware monthly and walk the device list every few months, removing what no longer exists.
Fifteen minutes a month keeps this useful. If you want a sense of where your overall exposure sits before spending anything more, our free Cyber Risk Check returns a prioritised list, and the Firewalla buyer’s guide compares the whole line.
Want it installed, monitored and patched for you? Managed Network & Infrastructure →
More in this category
- Firewalla Gold Pro: 10G Cyber Security Firewall & Router Protecting Your Family and Business
- Firewalla Gold Plus: 2.5G Cyber Security Firewall & Router Protecting Your Family and Business ()
- Firewalla Gold SE: Multi-Gigabit Cyber Security Firewall & Router Protecting Your Family and Business ()
- Firewalla Access Point 7 Ceiling: Enabling Zero Trust Network Security with Wi-Fi 7 and Firewalla
Reviews
There are no reviews yet.